
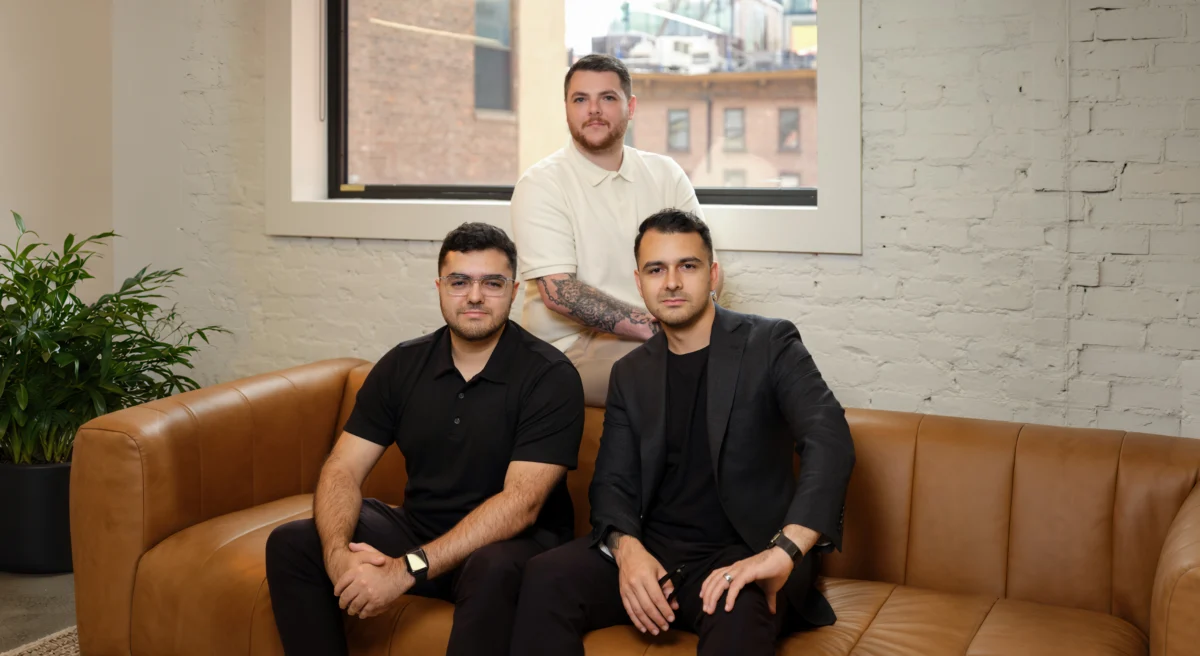
SAN FRANCISCO — In a resounding validation of AI-driven enterprise infrastructure, cybersecurity and compliance startup Comp AI announced on Thursday that it has successfully closed a $34 million Series A funding round. The financing was co-led by prominent venture capital firms Roo Capital and Grand Ventures, bringing the company’s total cumulative funding to an impressive $37.5 million since its inception in January of last year.
The capital injection arrives at a pivotal moment for the tech sector. As organizations rapidly integrate artificial intelligence agents into their core operational workflows, traditional, static methods of security auditing and compliance are straining under the weight of constant code deployments and autonomous decision-making systems. Comp AI aims to bridge this growing chasm by introducing an agentic platform designed to automate the most arduous aspects of regulatory compliance and proactive vulnerability testing.
Main Facts: A New Paradigm for Compliance
Comp AI operates at the intersection of generative AI and enterprise security. Founded by industry veterans Lewis Carhart, Claudio Fuentes, and Mariano Fuentes, the company has engineered an agentic platform that radically streamlines how businesses tackle compliance frameworks like SOC 2.
- Funding Milestone: $34 million Series A round co-led by Roo Capital and Grand Ventures. Total funding now stands at $37.5 million.
- Core Offering: An agentic AI platform that automates the drafting of security policies, collects evidence for security audits, continuously monitors regulatory controls, and performs AI-powered penetration testing.
- Founding Team: Lewis Carhart (CEO), Claudio Fuentes (COO), and Mariano Fuentes (CTO).
- Market Positioning: Positioned alongside established compliance automation platforms like Vanta and Drata, but uniquely tailored for the "agentic era"—where autonomous AI agents demand real-time governance, continuous monitoring, and strict permission boundaries.
- Operational Philosophy: Human-in-the-loop architecture. While AI agents draft policies and monitor controls, human workers retain ultimate authority to review, approve, and maintain workflows.
Chronology: From Pivot to Purpose
The story of Comp AI is rooted in the iterative journey familiar to many modern software entrepreneurs—a trajectory marked by experimentation, hard-learned lessons, and eventual product-market alignment.
The LeapAI Chapter
For nearly a decade, brothers Claudio and Mariano Fuentes built startups together. A few years ago, their paths crossed with Lewis Carhart. Impressed by his background and vision, the brothers invited Carhart to join LeapAI, a workflow platform they were developing at the time.
In this venture, Claudio served as CEO and co-founder, Carhart spearheaded growth as head of growth, and Mariano engineered the backend as a senior full-stack engineer. For roughly two years, LeapAI operated in the competitive workflow market, eventually scaling its user base to over one million users.
Despite the impressive user acquisition, the founders ultimately made the difficult decision to shut the platform down. They realized they had not found a "sticky enough use case to warrant continued investment." However, the failure proved to be a masterclass in enterprise software development.
Lessons in LLMs and the Pain of SOC 2
The LeapAI experience imparted two critical lessons to the founding trio. First, they gained deep, hands-on expertise in building with Large Language Models (LLMs) and learned the paramount importance of hyper-specific product use cases. Second—and perhaps more importantly—they experienced firsthand the administrative nightmare of achieving SOC 2 compliance.
As they attempted to scale LeapAI to secure larger enterprise clients, they hit a brick wall of regulatory red tape.
"It’s a very obscure process," Claudio Fuentes recalled. "It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product."
The Birth of Comp AI
Out of this operational bottleneck, the concept for Comp AI was born. Recognizing that compliance is often the ultimate gatekeeper for enterprise revenue—where a missing SOC 2 report can instantly stall a lucrative B2B deal—the trio decided to build the tool they wished they had during their time at LeapAI.
Drawing on the lessons of their previous startup, the founders structured leadership intentionally: because the core insight belonged to Carhart, he stepped up to lead the new venture as Chief Executive Officer, while Claudio took on the COO role and Mariano assumed the CTO position.
Supporting Data: The Economics and Mechanics of AI Compliance
The market dynamics favoring Comp AI are underpinned by hard financial realities and escalating technological complexities.
- Revenue Dependency: For software-as-a-service (SaaS) and enterprise tech companies, security and compliance are no longer back-office housekeeping items; they are existential revenue drivers. Enterprise procurement departments routinely require up-to-date SOC 2, ISO 27001, or HIPAA certifications before signing contracts.
- Funding Velocity: Securing a $34 million Series A is a rarity in the current venture capital climate, signaling profound investor confidence in the intersection of AI agents and cybersecurity infrastructure.
- Continuous Vulnerability: Modern businesses do not operate on static codebases. Companies frequently push dozens, if not hundreds, of code updates daily. Traditional compliance audits—which offer a static snapshot of a company’s security posture at a single point in time—are fundamentally misaligned with this velocity.
How the Platform Works
Comp AI’s software operates as a digital assistant and monitor. Rather than replacing human auditors or independent verification reviews, the platform handles the tedious heavy lifting:
- Policy Generation: AI agents draft comprehensive internal security policies tailored to specific compliance frameworks.
- Evidence Collection: The platform automatically gathers the technical artifacts and logs required by auditors, eliminating manual screenshots and document sorting.
- Continuous Monitoring: It tracks whether internal systems continuously meet regulatory controls.
- AI-Powered Penetration Testing: The platform proactively probes codebases and cloud infrastructures to unearth vulnerabilities before malicious actors can exploit them.
Official Responses and Strategic Vision
Leadership at Comp AI emphasizes that while automation is the core value proposition, the platform is built with strict guardrails that prioritize human oversight.
Balancing Automation with Human Accountability
As artificial intelligence agents take on increasingly consequential roles—such as directly accessing customer databases or altering internal system permissions—the need for rigorous governance multiplies.
"An agent might draft a policy, for example, but a person still reviews and approves it," Lewis Carhart explained during an interview. "As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly."
This human-in-the-loop philosophy extends to how companies onboard the AI. Human workers actively support security controls and maintain agentic workflows, ensuring that the technology acts as a force multiplier rather than an unmonitored loose cannon.
Addressing the Real-Time Security Gap
Carhart highlighted a critical vulnerability in the traditional compliance lifecycle that legacy tools fail to address:
"Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment," Carhart said. "The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward."
Echoing this sentiment, Mariano Fuentes noted that as corporations adopt more autonomous systems, they face mounting pressure from regulators and stakeholders to provide transparent logging of agent behavior.
"We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve," Mariano stated, emphasizing that Comp AI is fundamentally tackling the challenge by anchoring its architecture in permissions and accountability.
Implications: Navigating the Agentic Era of Cybersecurity
The successful funding round for Comp AI shines a light on broader structural shifts occurring across the global tech landscape.
1. The Crowded Compliance Landscape
Comp AI enters a market already populated by established compliance automation heavyweights such as Vanta and Drata. However, while legacy automation tools focused primarily on connecting to cloud services to check off static compliance boxes, the next generation of security startups—led by firms like Comp AI—must account for the fluid, unpredictable nature of autonomous AI agents.
2. Redefining Enterprise Risk Management
The proliferation of agentic workflows means that software is no longer passive; it executes decisions, writes code, and interacts with sensitive data streams independently. Consequently, security infrastructure must evolve from point-in-time auditing to continuous behavioral validation. Startups that successfully master this transition will likely capture substantial market share as enterprises scramble to secure their internal AI deployments.
3. Capital Allocation and Product Expansion
With $37.5 million in total funding now at its disposal, Comp AI’s executive team plans to aggressively scale its engineering and go-to-market teams. The newly acquired capital will directly fund product expansion, deepening the platform’s ability to handle complex automated penetration testing and advanced agentic governance frameworks.
Conclusion
As businesses race to harness the productivity gains of artificial intelligence, the margin for security error narrows dramatically. By turning the painful lessons of their past startup failures into a streamlined, AI-native compliance engine, the founders of Comp AI have positioned their company at the vanguard of enterprise security. With institutional backing from Roo Capital and Grand Ventures, Comp AI is well-equipped to help the corporate world navigate the complex, high-stakes waters of the agentic era.
 rifanmuazin
 Nana Muazin
